Security checks.
Assisted by local AI.
A defensive cybersecurity tool developed at NO STUDIO, assisted by a local large language model (LLM) through Ollama. Interpret technical evidence, understand findings and keep follow-up work connected in one persistent terminal workflow.
For systems you own or are authorised to assess.
A check is
a starting point.
Keep the technical output, understand what it means and return to it as the work progresses.
Checks
- Controlled Nmap workflows for network and service discovery.
- DNS, HTTP, TLS, security-header and cookie checks.
- Bounded website audits and optional Nuclei vulnerability scanning.
Evidence
- Local LLM support for interpreting scan output and authentication, web and firewall logs.
- Local records of assets, scans, raw evidence and findings.
- Finding deduplication, observation history and triage.
Follow-up
- Remediation tracking linked to recorded findings.
- Baselines, comparisons and fresh evidence after retesting.
- Reporting to support review and the next steps.
Collect. Review.
Remediate. Retest.
Collect evidence
Run authorised checks and keep the technical output alongside records of the assets and scans.
Review findings
Use the local LLM to help explain findings, then review its interpretation against the supporting evidence and decide what needs attention.
Remediate
Track the follow-up work and the status of each finding as changes are made.
Retest
Collect fresh evidence, compare it with the baseline and review the result before resolving a finding.
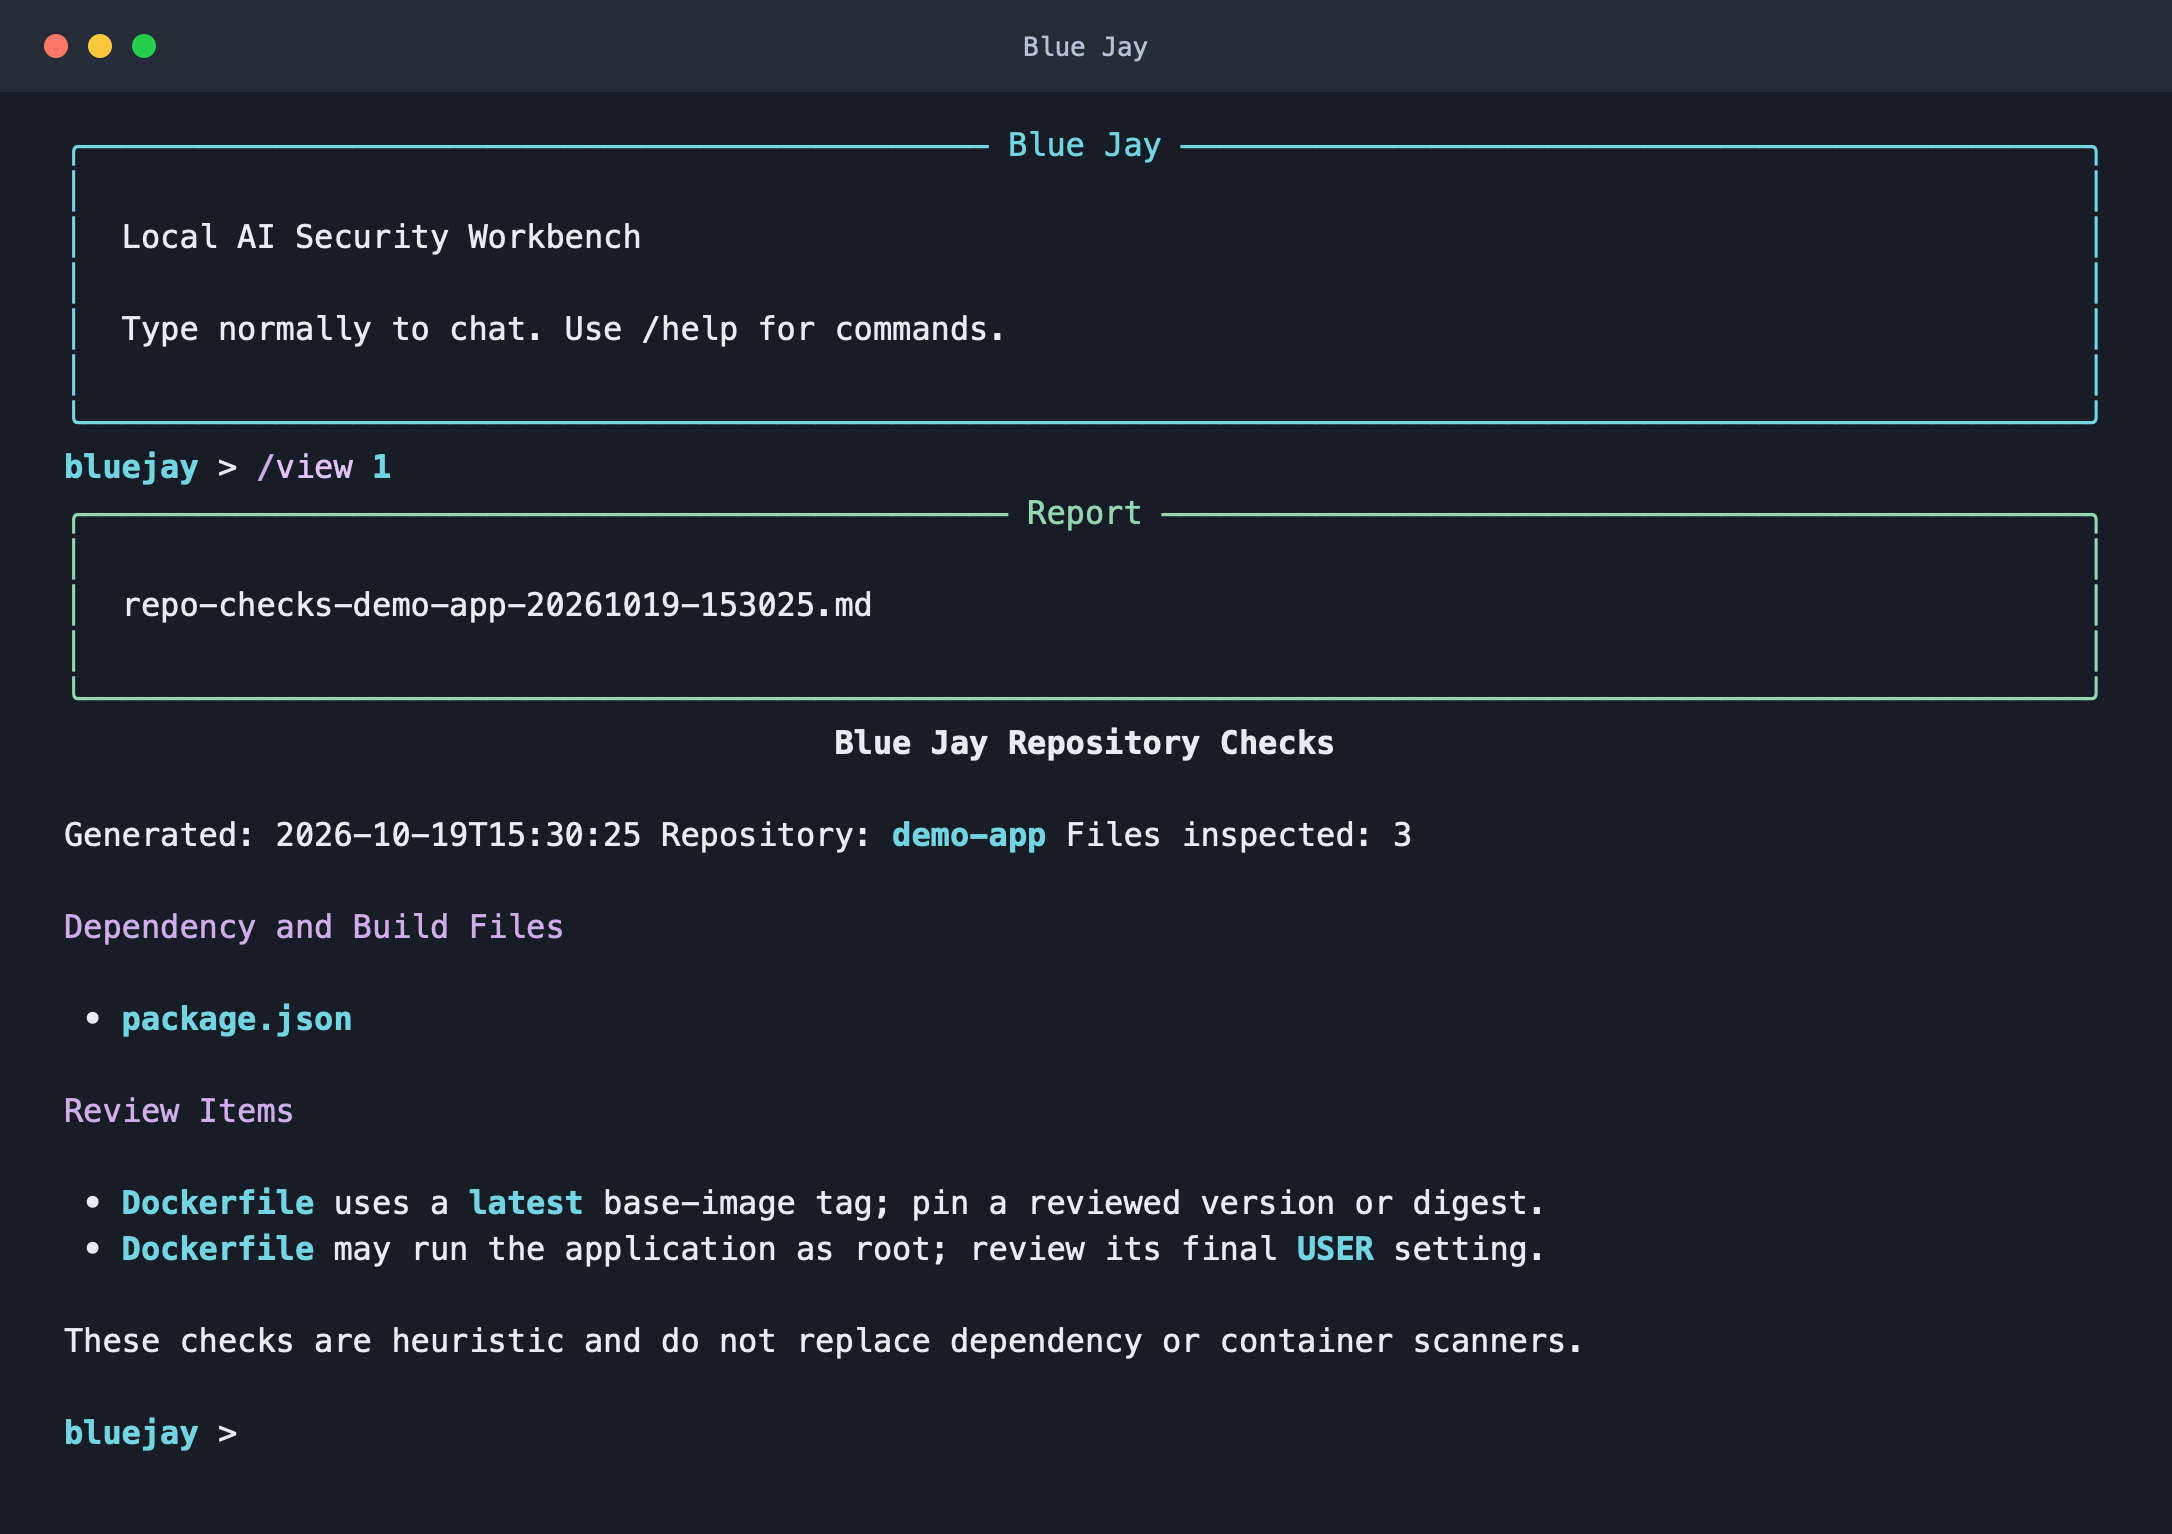
An example report. Rendered from Blue Jay terminal output using a local demo repository, with a window frame added for presentation. The checks flag items for human review.
Open full-size reportLocal models.
Human judgement.
Local-first means runtime data is stored locally and LLM analysis runs on your machine through Ollama. Security checks still contact authorised targets and relevant network services.
- Controlled execution
- The application validates inputs, controls tool execution and preserves the evidence. The AI does not receive direct shell access.
- Local LLM interpretation
- Large language models run through Ollama on your machine to help explain evidence and findings.
- Evidence and explanation
- Raw evidence remains separate from model-generated explanations. Important claims and suggested actions require human review.
A closer look.
With people behind it.
NO STUDIO offers security analysis for websites and applications within an agreed scope. Blue Jay is our own internally developed tool, with professional judgement and human review central to the work.
Findings need to be assessed in context. A clean result is not confirmation that a system is secure.